💻
💻 Technology
Hundreds of millions of Broadcom routers vulnerable to Wi-Fi attacks
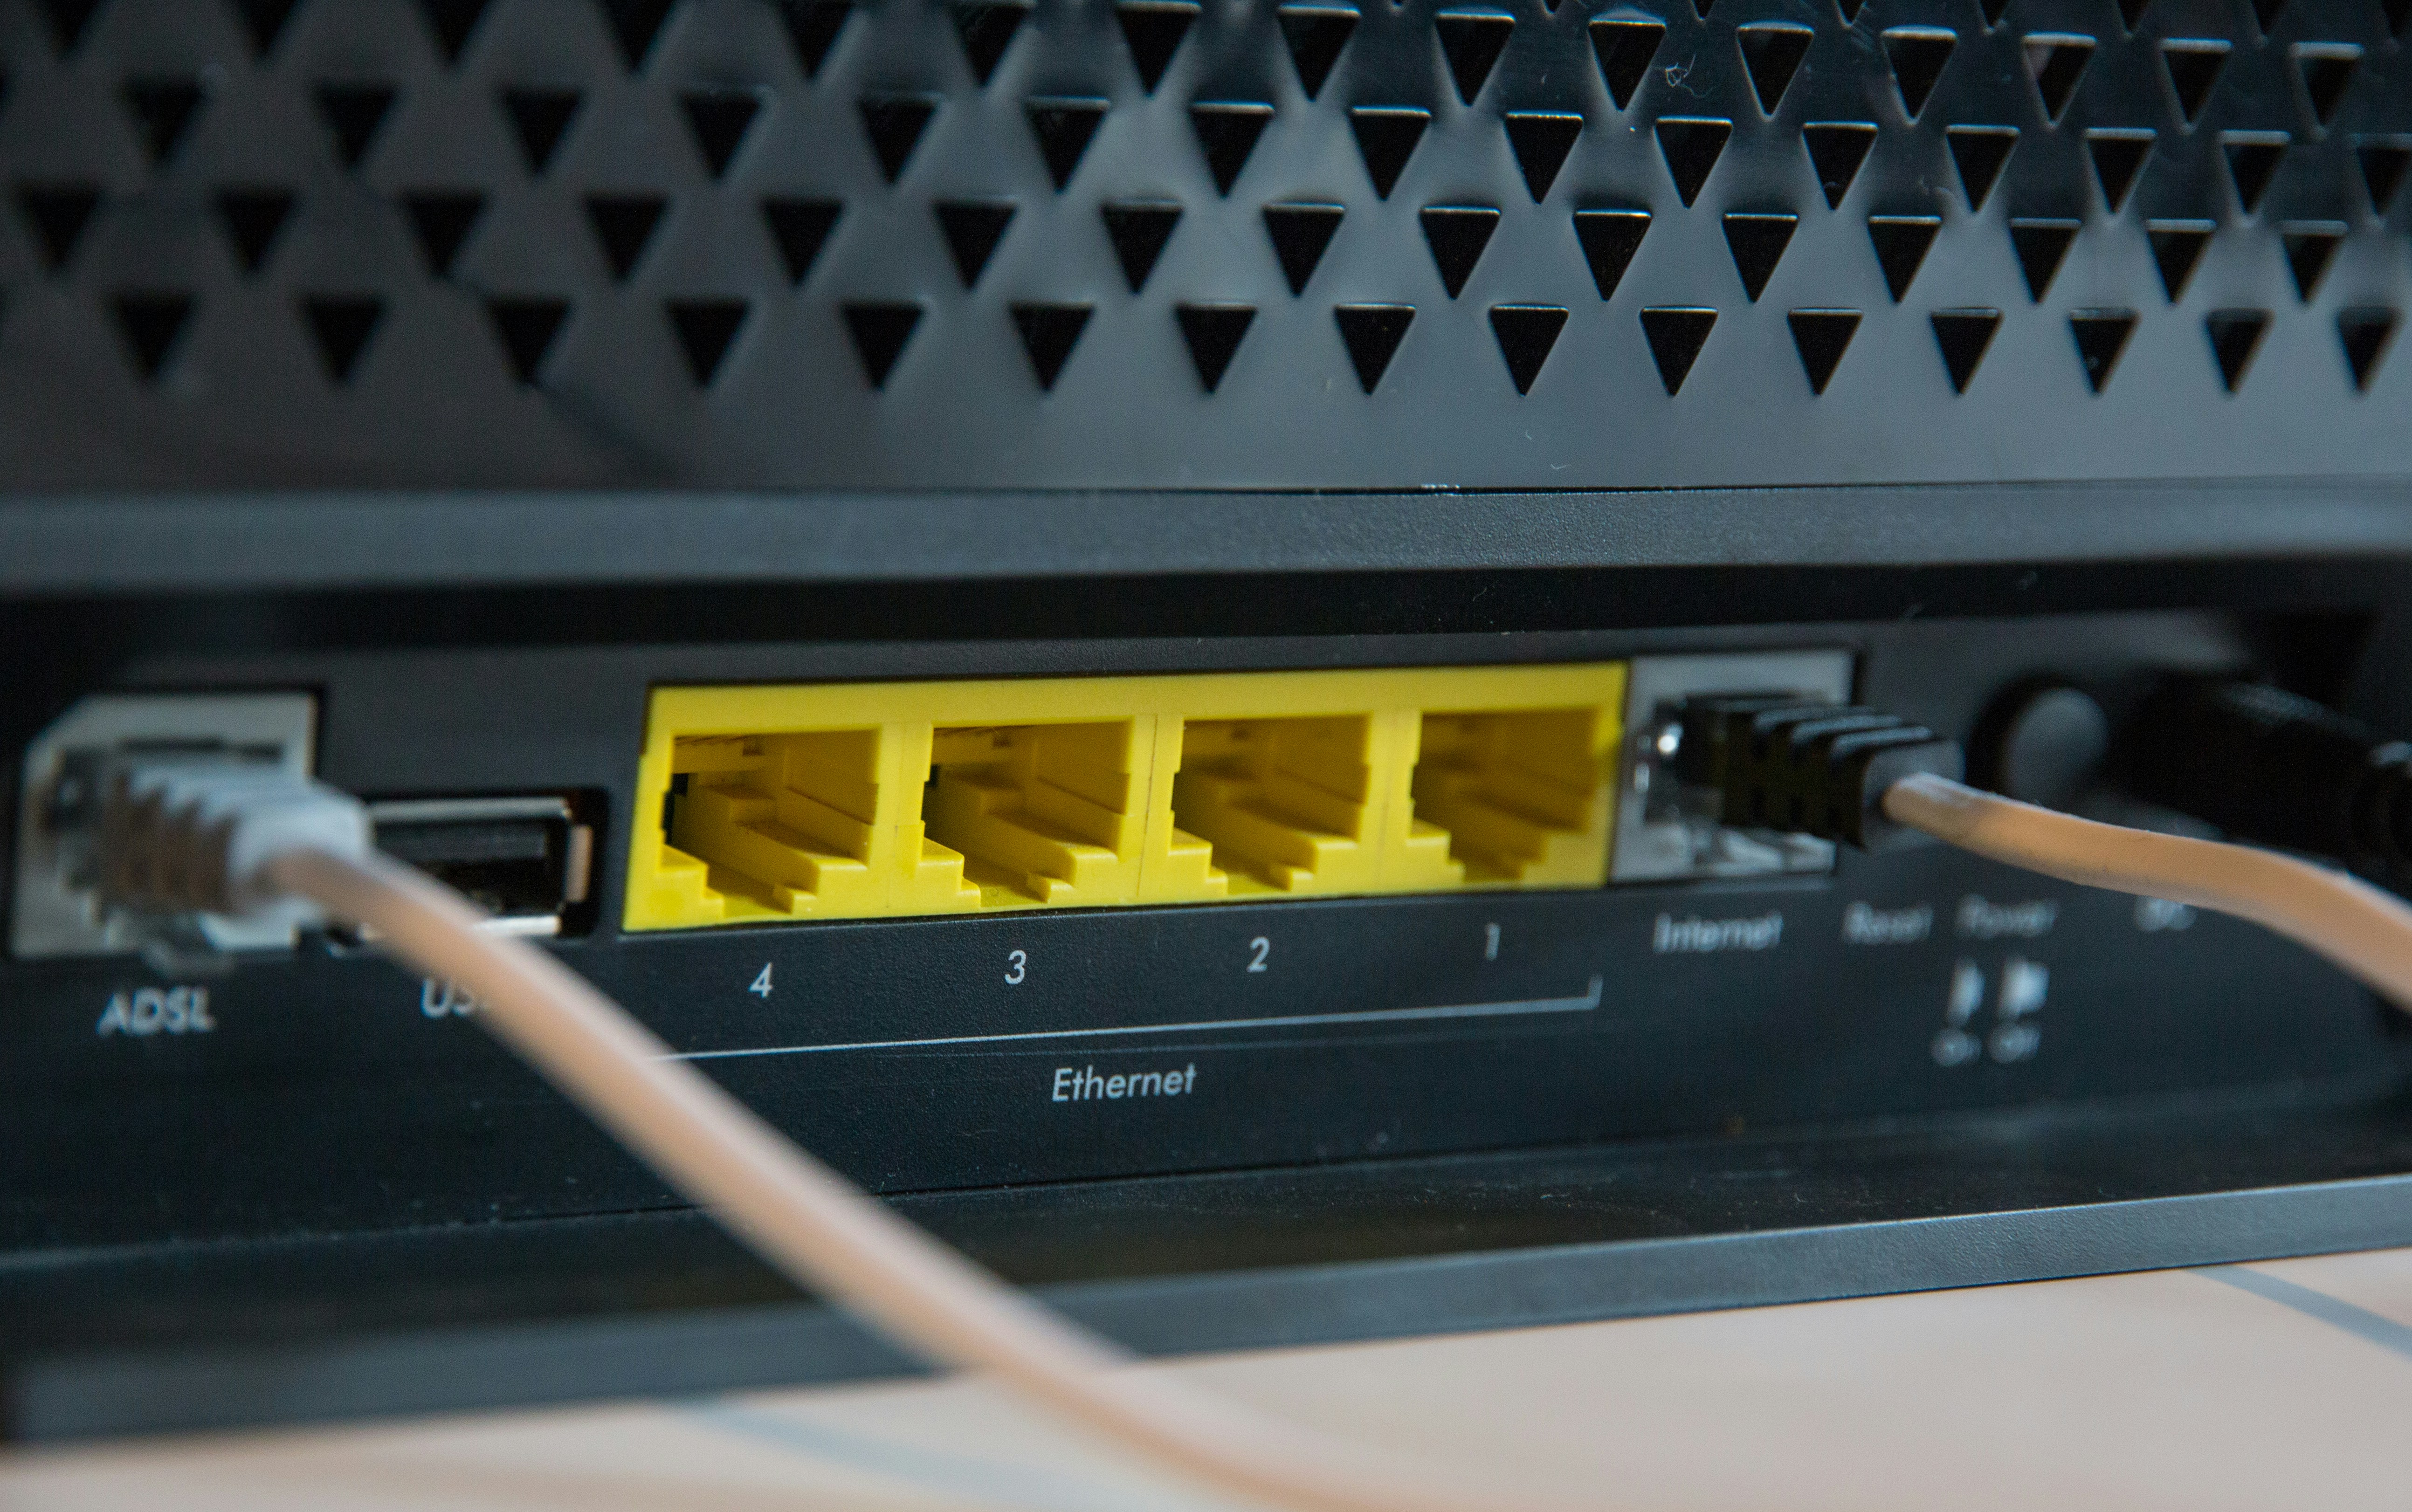
Security researcher Quentin Kaiser discovered a flaw in Broadcom firmware that has existed since 2010 and affects hundreds of millions of routers from multiple manufacturers worldwide. The vulnerability allows an attacker to take control of a device over Wi-Fi without knowing the password or WPS configuration, and can execute arbitrary code — turning the router into a spying tool or part of a DDoS network. Broadcom was aware of the problem but did not disclose it.
Comments
No comments yet

Comments
No comments yet — be the first to weigh in 👇
No comments yet. Be the first!